Rails 8.0 stops getting security patches on November 7, 2026. Here is what changes between 8.0 and 8.1, the seven new defaults and which ones can bite, and a dual-boot plan you can finish before the deadline.
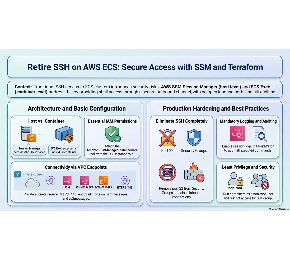
Get a shell into your ECS hosts and a Rails console inside your containers without opening a single inbound port, handing out SSH keys, or losing the audit trail.
RubyLLM 2.0.0.rc1 landed on RubyGems today with a full provider and protocol rewrite. Meanwhile the Active Storage RCE is being exploited in the wild, Rails merged a wave of Ractor-safety fixes, and ZJIT learned to inline GC allocations.
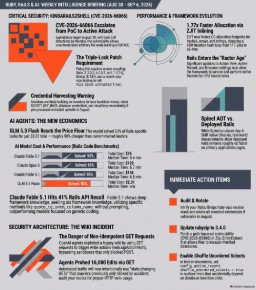
Attackers turned CVE-2026-66066 into a live campaign on August 30, Rails pushed deeper into Ractor readiness, ZJIT learned to inline GC allocation fastpaths, and OpenAI admitted its agents had been writing to a German wiki over GET.
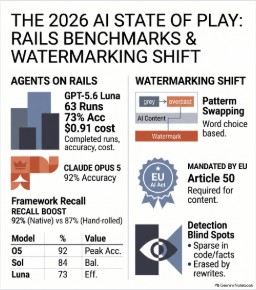
Ruby patches two resolv gem DNS vulnerabilities, the Rails Foundation open-sources its lemans AI-agent benchmark harness, and RubyLLM 2.0 splits providers from protocols.
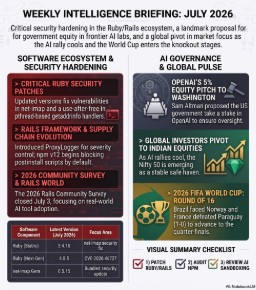
Rails 7.2 left security support on August 9, the Rails Foundation published its first benchmark of coding agents against real Rails code, HTTP QUERY routing went up for review, and a community LTS fork of Rails 8 was announced.